Website Tracking Compliance

Website Tracking Compliance Review

Review how cookies, tracking scripts, pixels, analytics tools, consent behavior, third-party requests, and privacy disclosures appear to work across real website visits.

  • Understand how website tracking compliance is reviewed in practice
  • Identify tracking risks involving cookies, pixels, scripts, and third-party tools
  • Use technical evidence to support internal, legal, or compliance review

Want a broader review of privacy and tracking behavior? Use a broader website privacy audit.

Evidence-first tracking compliance guide

Built for teams that need to understand how cookies, trackers, pixels, and third-party requests affect website compliance review.


Tracking-first review for websites and digital products

Useful for founders, privacy teams, agencies, consultants, SaaS teams, and ecommerce teams

Designed for live behavior, not only policy review

Helpful before audits, remediation, launches, campaign changes, or vendor updates

What is website tracking compliance?

Website tracking compliance is the review of how a website uses cookies, analytics tools, advertising pixels, embedded technologies, scripts, and related identifiers during real visits. In practice, this means looking not only at privacy policies or banners, but also at what the site actually appears to do when pages load, forms are used, or third-party services activate.

A useful tracking compliance review focuses on technical behavior, consent flow, third-party visibility, and whether website disclosures align with what can be observed through live testing.

Why tracking compliance matters

Many websites depend on analytics, marketing tools, pixels, session technologies, and embedded services to operate or measure performance. But without structured review, teams may not have a clear view of what data is collected, when tracking begins, which third parties receive requests, or whether users are given meaningful control where required.

Why teams review tracking compliance
  • Understand how trackers behave during live visits
  • Review consent-related risk areas before scaling campaigns
  • Map third-party technologies, vendors, and request destinations
  • Compare technical behavior to privacy and cookie disclosures
What surface checks often miss
  • Scripts may load before meaningful user choice
  • Third-party tools may receive identifiers indirectly
  • Policies may not reflect actual tracker behavior
  • Different pages, forms, campaigns, or consent states may behave differently

What website tracking compliance review includes

A practical website tracking compliance review usually covers the technologies that appear during page visits, how they behave across consent states, and whether what they do aligns with the site's intended controls and disclosures.

Cookies and storage technologies

Review browser cookies, local storage, session storage, and other client-side mechanisms that may support tracking or identifier persistence. If cookies are your main concern, you can also review cookie and tracker behavior directly.

Analytics and measurement scripts

Review tools used for website analytics, audience measurement, conversion tracking, behavioral observation, or marketing performance reporting.

Advertising pixels and marketing technologies

Review external ad-tech or marketing tools that may activate during page visits, form submissions, checkout flows, retargeting campaigns, or user interactions.

Consent and preference flows

Review how tracking behavior appears before consent, after acceptance, after rejection, and after preference changes where those choices are available.

Third-party requests and recipients

Review which domains, services, vendors, or external systems appear to receive user-related requests during website visits.

Disclosure consistency

Compare privacy notices and cookie disclosures with the website's observed technical behavior so mismatches can be reviewed by internal, legal, or compliance teams.

Tracking compliance expectations can vary depending on user location, business model, data practices, and applicable frameworks such as GDPR, CCPA/CPRA, CIPA-related risk analysis, or cookie consent rules.

What technical evidence can support a tracking compliance review?

Tracking compliance review becomes more useful when findings are tied to observable website behavior. Instead of relying only on policy language or banner text, teams can review what actually appears to happen during page loads, consent choices, form interactions, and third-party requests.

Cookie and storage observations

Document which cookies, local storage entries, or session storage items appear during different visit and consent states.

Third-party request behavior

Review external domains, request patterns, and vendor connections that may appear when scripts, pixels, or embedded tools activate.

Consent-state comparisons

Compare what happens before consent, after acceptance, after rejection, and after preference changes where the website provides those controls.

Review-ready documentation

Useful evidence may include screenshots, cookie records, request logs, HAR or network observations, vendor notes, and report findings that support remediation planning.

Want to see how findings are documented?

Preview how Auditzo organizes cookies, trackers, consent behavior, third-party scripts, privacy policy gaps, and evidence-backed observations into a structured report.

Website tracking compliance checklist

A simple checklist can help teams review tracking behavior before campaigns, audits, consent-banner changes, vendor updates, or privacy policy reviews.

  • Inventory cookies, local storage, and session storage entries
  • Review analytics scripts, tag managers, and marketing pixels
  • Test what loads before users make a consent choice
  • Compare behavior after accept, reject, and preference changes
  • Map third-party request domains and likely vendor relationships
  • Check whether privacy and cookie disclosures match observed behavior
  • Review form, signup, checkout, and campaign landing page behavior
  • Recheck tracking after new scripts, campaigns, or CMP changes

For a more cookie-focused workflow, use the cookie audit checklist.

Common website tracking compliance issues

Many tracking-related problems are not obvious without live testing and structured technical review.
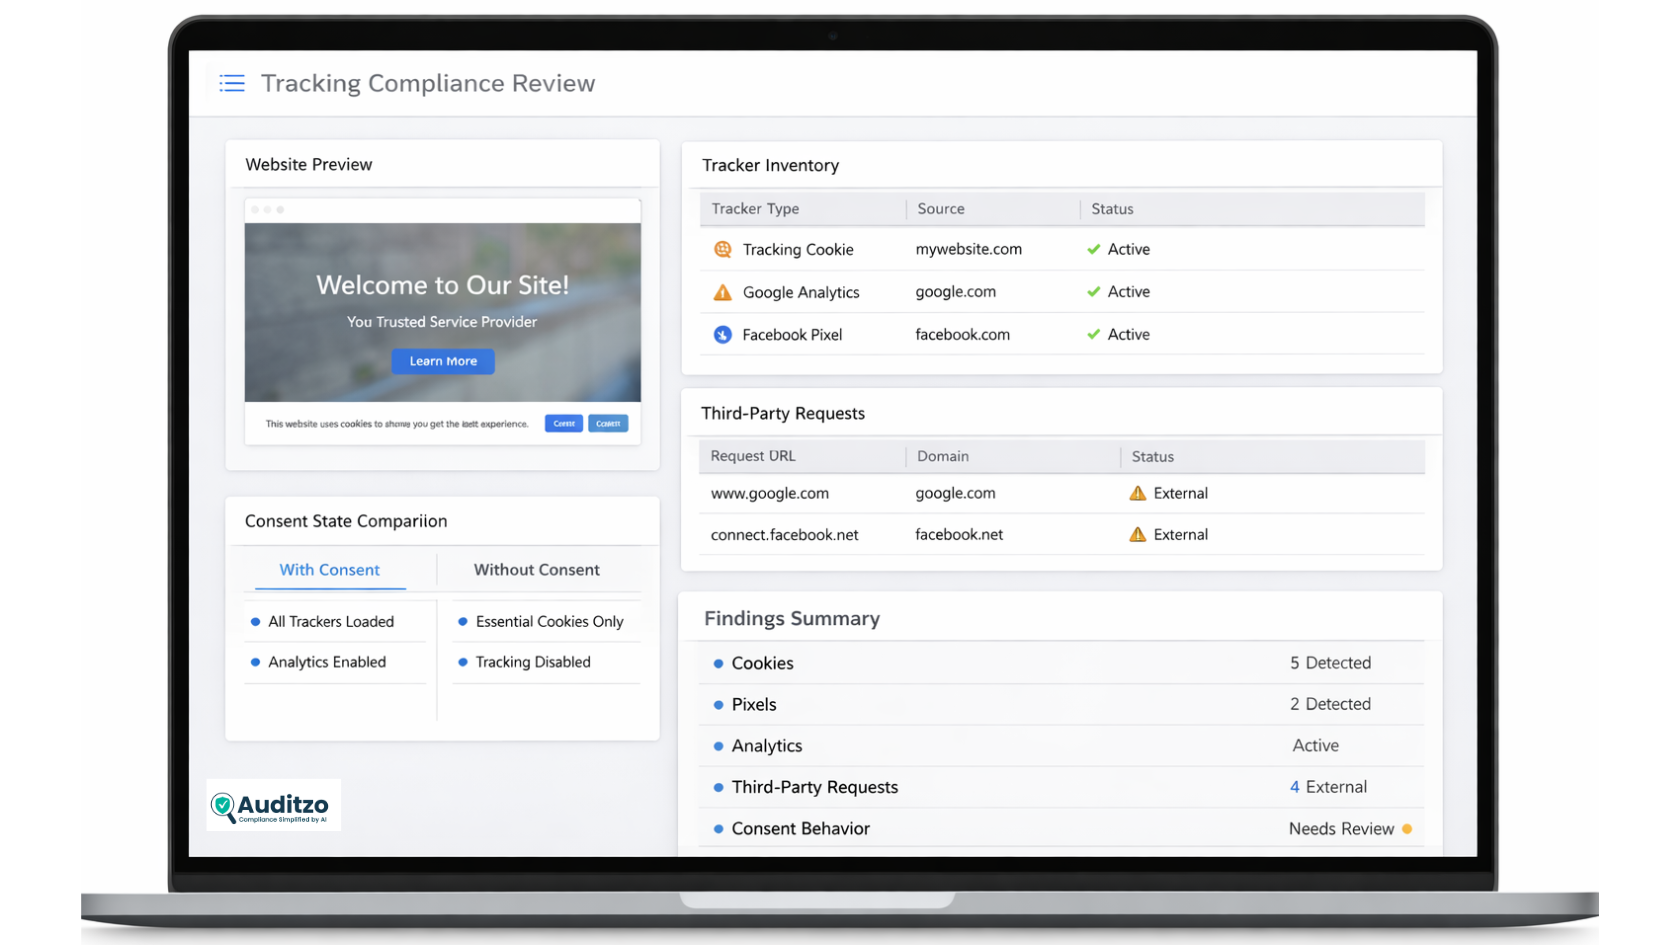
Website tracking compliance preview showing cookies, trackers, third-party requests, and consent-related review items

Example view of tracker activity, third-party requests, consent-related states, and website compliance review findings.

When to review website tracking behavior

Tracking behavior can change without obvious design changes. A new campaign, analytics tag, embedded widget, consent setup, or vendor integration may affect what loads during real visits.

  • Before launching paid campaigns or retargeting pixels
  • After adding analytics, chat, heatmap, CRM, or tag manager tools
  • Before entering EU, California, or other privacy-sensitive markets
  • After changing a cookie banner, consent manager, or preference center
  • Before legal or compliance teams review your website setup
  • After redesigning forms, checkout flows, or signup journeys
  • When privacy disclosures no longer clearly match your marketing stack
  • When agencies or vendors manage tracking tools on your behalf

Periodic review can help identify tracking changes over time, but this page should not be read as legal advice or a guarantee of compliance.

Move from tracking guidance to live website review

If you understand the tracking risks and want to review your own website behavior, Auditzo can help you move from general guidance to structured technical observations.

Website compliance checker

Review broad website behavior across cookies, scripts, trackers, consent states, and third-party requests.

Use Website Compliance Checker
Cookie audit tool

Review cookie and tracker behavior during live visits, including consent-related behavior where available.

Run Cookie Audit Tool
Sample audit report

See how cookies, trackers, consent behavior, third-party scripts, and privacy gaps are organized into an evidence-backed report.

View Sample Audit Report

Frequently asked questions

Website tracking compliance is the review of how cookies, pixels, analytics scripts, third-party tools, and related identifiers behave during real website visits.

It usually includes cookies, local storage, tracking pixels, analytics scripts, consent behavior, third-party requests, and whether disclosures match observed behavior.

Yes. Tracking pixels used for ads, analytics, retargeting, or conversion measurement should be reviewed to understand when they load and what third-party requests they trigger.

They may create risk if they load before user choice, send identifiers to external services, or behave differently from what the website’s privacy or cookie disclosures describe.

Because some cookies, pixels, or scripts may behave differently before consent, after acceptance, after rejection, or after preference changes. These states should be tested separately.

Useful evidence may include cookie records, storage entries, third-party request logs, consent-state comparisons, screenshots, and HAR or network observations where deeper review is needed.

No. Auditzo provides technical observations and evidence-backed website audit reports to support internal review, remediation, and legal or compliance discussions. It does not provide legal advice or guarantee compliance.

Need to review live tracking behavior on your website?

Use Auditzo to review how cookies, pixels, third-party technologies, consent states, and related requests appear to behave during actual website visits.

Move from tracking concern to evidence-backed review

Start with a live website review, or preview the report format first to see how Auditzo documents cookies, trackers, scripts, consent behavior, and third-party requests.

Auditzo provides technical website behavior review and evidence-backed observations. It does not provide legal advice or guarantee compliance.