See what cookies, scripts, and third-party requests are observable during an initial website visit. This free GDPR-focused check provides a technical starting point; controlled Accept/Reject consent testing is available through a scoped manual review.
No code changes. No backend access. Public website behavior only. Not sure whether GDPR is the right framework? Use the Compliance Framework Finder .
Auditzo provides technical observations and compliance posture support based on observable website behavior. It does not provide legal advice or guarantee GDPR compliance.
Initial, no-interaction website scan of observable cookies, scripts, and third-party requests. Accept/Reject journeys and form submissions are not tested.
When the free scan is not enough
A cookie banner can look correct while third-party requests behave differently. Start with an initial website scan, or request a defined manual investigation when you need evidence of what happens after a visitor accepts or rejects consent.
A technical snapshot of observable behavior during the first public website visit.
A scoped technical review for teams who need to verify consent implementation behavior.
Manual evidence audits start at $899; final scope and pricing depend on the investigation.
See relevant project experience: European multi-site tracking and consent evidence review .
Auditzo provides technical observations, not legal advice or a GDPR compliance certificate. A website-level review does not assess an organization's full GDPR obligations.
Auditzo helps teams move from general GDPR uncertainty to a clearer view of cookies, trackers, forms, third-party behavior, and website activity that may affect consent and data handling expectations.
Designed specifically for GDPR-related website review and reporting.
Surfaces cookies, trackers, and third-party requests observed during the initial visit; consent-choice journeys require manual review.
Structured findings based on what the website appears to do, not just what banners or policies suggest.
Useful for internal review, remediation planning, and follow-up with legal or compliance teams.
No public website check can confirm full GDPR compliance on its own. GDPR compliance depends on legal, operational, contractual, and technical factors. However, a website GDPR compliance check can help identify visible behavior that may need review.
Auditzo helps document technical observations so your team can review them internally or with legal and compliance professionals where needed.
This page is designed for teams that want to review website GDPR compliance by looking at how a site behaves in practice, especially where cookies, analytics, forms, marketing tools, and third-party services may affect personal data handling.
Website GDPR compliance depends on what personal data is collected, how cookies and trackers behave, where data is transmitted, and whether users are given meaningful control before certain technologies activate. A website can appear compliant on the surface while still behaving differently during real visits.
This page is informational and intended to explain website GDPR compliance review in general terms.
A comprehensive GDPR website review looks beyond whether a privacy policy or cookie banner exists. The free Auditzo scan captures initial observable activity; scoped manual reviews can examine selected consent choices, forms, and disclosure alignment in greater detail.
Checks whether cookies, trackers, analytics scripts, or marketing pixels appear before a user gives meaningful consent.
Identifies third-party tools, external domains, tag managers, embedded services, and technologies that may receive requests during page loads.
A scoped manual review can examine selected contact, signup, checkout, or newsletter journeys. The free scan does not submit forms.
A broader manual review may compare observed tracking behavior with published privacy and cookie disclosures to identify items for further assessment.
Many GDPR compliance issues originate from cookies and tracking technologies that activate before users provide consent. These issues are often not obvious from a banner setup or policy review alone. If you specifically want to review how cookies behave on your website, you can also run a GDPR cookie compliance check .
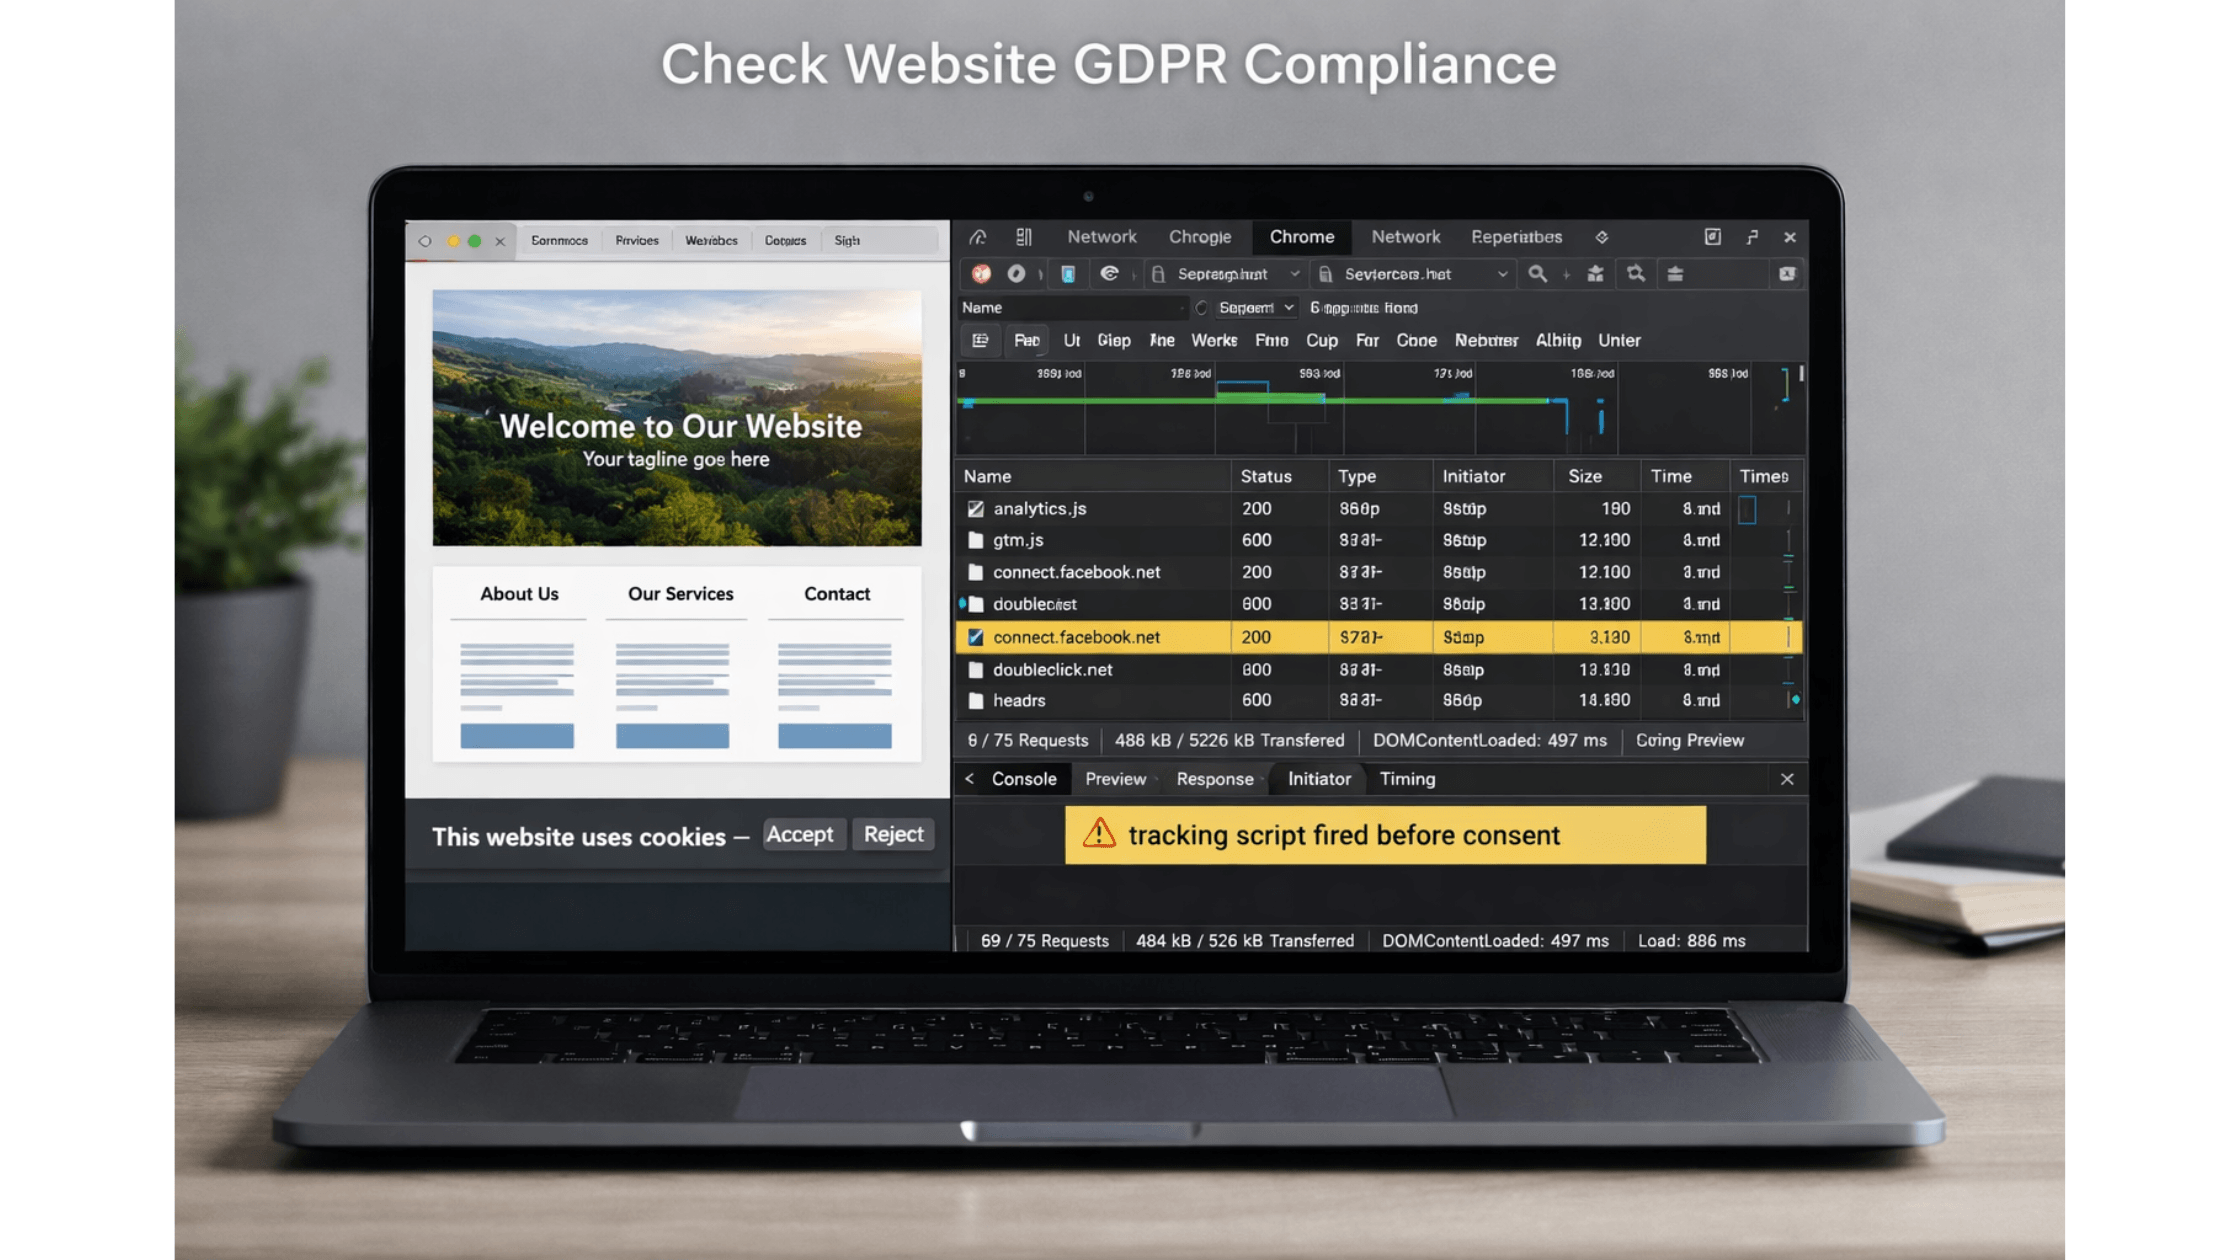
Example view of cookies and tracking scripts that may activate during a website visit before meaningful consent is captured.
Analytics scripts, marketing pixels, or cookies may activate before a user has made a meaningful choice.
External services may receive data during page loads, sometimes through indirect integrations, embedded tools, or tag managers.
Privacy or cookie policy language may not fully reflect what the website actually does during normal use.
New tools, scripts, consent settings, campaign tags, or marketing changes can alter compliance posture without obvious visual changes on the site.
For more context on consent expectations, you can also review Auditzo’s guide on GDPR cookie consent rules .
The automated scan records initial observable website activity. Scoped manual audits can go further into selected consent interactions and technical evidence. If you want a more detailed framework page, see GDPR compliance audit for websites .
Focuses on what the website appears to do during normal user visits, not just what is disclosed in policies, banners, or consent messages.
Helps surface scripts, cookies, trackers, marketing pixels, analytics tools, and third-party activity that may affect consent expectations.
Reviews how personal data or user identifiers may appear to move through website components and third-party connections.
Findings are organized for internal review, follow-up, remediation planning, and discussion with legal or compliance teams where needed.
Different review types serve different purposes. A GDPR checker can help identify visible website behavior, while a broader audit may provide deeper documentation and remediation context. Legal interpretation should remain with qualified legal or compliance professionals.
Provides an initial no-interaction snapshot of observable cookies, scripts, trackers, and third-party requests. It does not click Accept/Reject or submit forms, and it is not a legal certification.
A scoped manual review can test selected consent choices and journeys, document observed third-party activity, and provide evidence-linked findings and remediation priorities.
Uses technical observations to assess obligations, risk, and next steps. Auditzo does not replace legal counsel or guarantee GDPR compliance.
Available evidence depends on the type and scope of review. The free automated scan observes the initial visit; human-reviewed investigations can include additional consent states and user journeys when agreed.
Depending on the audit depth, technical observations may support digital evidence for compliance reviews , including browser-level behavior, network-level observations, screenshots, and structured findings where applicable.
After the free initial-state scan, Auditzo provides a GDPR-focused screening report. More detailed consent-state evidence and remediation findings are available through an agreed manual review.
Structured sections organized around GDPR-related website behavior and review areas.
Observations covering cookies, scripts, trackers, forms, and third-party activity during real visits.
Based on initial page-load activity in the free scan; selected website interactions may be documented in a scoped manual review.
Written to help product, marketing, ops, founder, legal, and compliance teams understand the findings.
Reports are designed to support internal review, remediation planning, developer handoff, and discussions with legal counsel where needed. They should not be treated as legal advice or a guarantee of GDPR compliance.
You can view a sample website privacy compliance audit report to understand how findings may be organized.
A website GDPR compliance check is especially valuable when tracking setup, data collection methods, consent configuration, or regional user exposure changes over time.
For an example of how website compliance reviews can support real business decisions, see this GDPR and CCPA compliance audit case study .
Use a short assessment to identify which privacy and data protection frameworks may be relevant based on your business model, website setup, and user regions.
Start a GDPR-focused website compliance check and receive a structured report by email.
Need to verify what happens after Accept or Reject? Explore human-reviewed consent verification.