Screenshots, Logs, and HAR Files: What Each Website Tracking Evidence Format Can Document
Website tracking reviews often produce several kinds of technical artifacts: screenshots, browser-network records, HAR files, cookies, browser-storage observations, console messages, DNS records, proxy captures, and evidence indexes.
These artifacts are not interchangeable. A screenshot may clearly show what was visible on a page, while a HAR file may preserve details about browser-observed network requests. A cookie record may show that a value existed in browser storage, while a proxy or server log may document a different layer of the same interaction.
The quality of a technical evidence set depends less on selecting one supposedly superior format and more on documenting scope, session conditions, timing, artifact relationships, file handling, and limitations.
This guide explains what screenshots, logs, and HAR files may help document in a website tracking review, what each format cannot establish by itself, and how law firms, privacy teams, developers, and technical reviewers can organize them into a traceable evidence set.
Key point: No artifact is automatically complete, authentic, admissible, or legally conclusive merely because it is a screenshot, log, HAR file, or hashed file. Technical artifacts document observations made within a defined environment and session. Their legal significance remains a separate matter for qualified counsel.
Screenshots, Logs, and HAR Files Are Not Interchangeable
A website interaction takes place across multiple technical layers. What appears on the screen is only one layer. The browser may simultaneously load scripts, send requests, receive responses, store cookies, update local storage, generate console messages, and communicate with first-party or third-party systems.
Different artifacts preserve different parts of that activity:
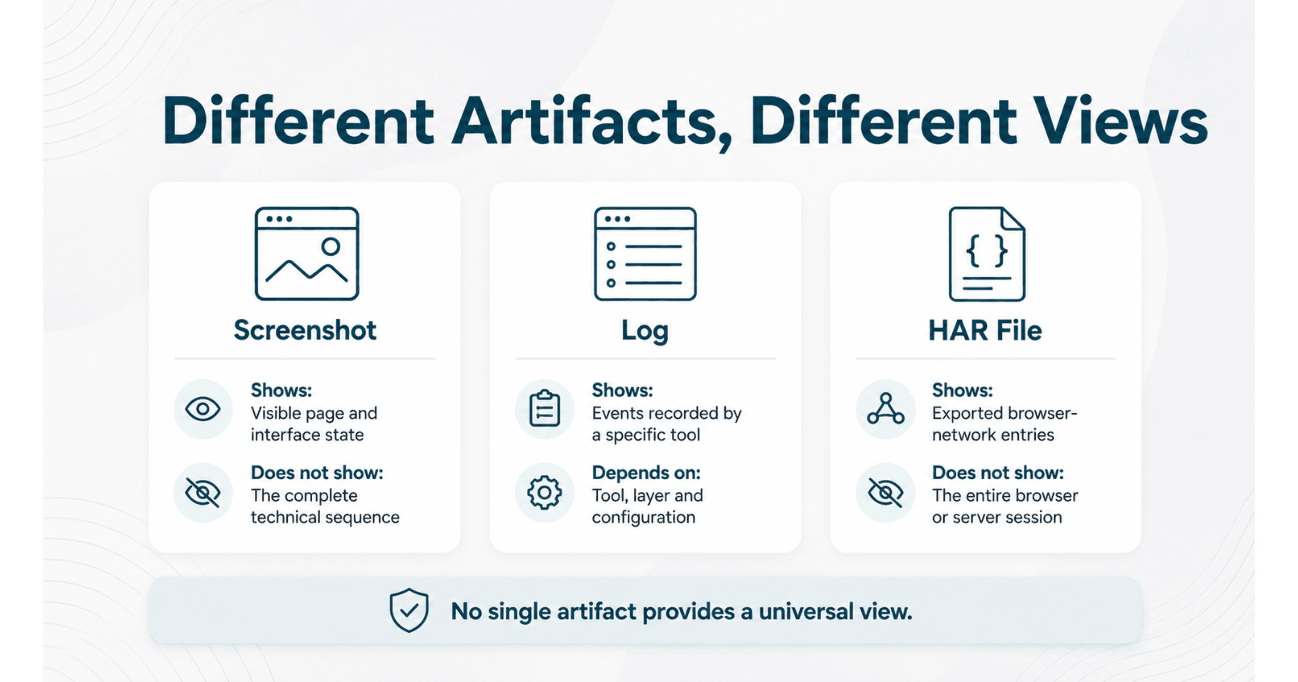
- Screenshots preserve visual context at a particular moment.
- Browser-network logs show requests observed in the browser’s Network tool.
- HAR files export structured information from a browser-network log.
- Console logs may show browser messages, script errors, warnings, or developer output.
- DNS records may show domain-resolution activity.
- Proxy captures may observe traffic passing through the configured proxy layer.
- Server logs may document activity received or generated by systems controlled by the website or vendor.
- Cookie and storage records show selected browser-side values present at a defined point in the session.
None of these formats provides a universal view of everything that occurred.
A useful evidence package therefore begins with a narrower question:
What specific observation are we trying to document, and which artifact or combination of artifacts supports that observation?
For broader reliability criteria, review Website Tracking Evidence Reliability: A Technical Review Checklist.
What Screenshots Can Document
A screenshot is a visual record of what appeared within the captured interface at a particular moment. Depending on the capture method, it may show the website, browser chrome, developer tools, a consent interface, a form, an embedded service, or a selected network request.
Visible page state
A screenshot may help document:
- The page that was reviewed
- The visible URL or browser address bar
- Whether a consent interface was visible
- The choices presented by the consent interface
- A selected consent preference
- A form, chatbot, video player, map, or embedded widget
- A visible error or unexpected page behavior
- A particular step in an agreed user journey
Developer-tool context
A screenshot may also preserve a visible developer-tool state, such as:
- A selected Network request
- A visible request hostname
- A request timing value
- Selected headers or parameters
- A cookie displayed in the browser’s storage panel
- A console warning or error
This can help a reviewer understand why a finding was recorded and where the related technical detail appeared.
Useful screenshot context
A stronger screenshot record commonly includes or is associated with:
- Page URL
- Capture date and time
- Time zone
- Browser and version
- Viewport or device profile
- Consent state
- Session identifier
- Short description of the action performed
- Reference to the associated request, cookie, storage item, or finding
A screenshot filename such as screenshot-17.png provides little context by itself. A filename or index entry such as reject-session-product-page-consent-banner-001.png is easier to review and cross-reference.
What Screenshots Cannot Establish by Themselves
A screenshot preserves what was visible within the captured frame. It does not automatically preserve the complete technical sequence that produced the visible state.
A screenshot alone generally cannot establish:
- Every request made before or after the image was captured
- The complete request or response body
- Whether a request was blocked, cached, retried, redirected, or later repeated
- What occurred outside the visible browser or developer-tool panel
- What happened on a server after a request was received
- How a third party subsequently processed or shared information
- Whether the displayed page state was typical across other browsers, regions, users, or sessions
- Whether a user legally consented
- Whether a statutory requirement or exception applies
- Whether the screenshot is legally authentic or admissible
A missing visible banner is a scoped observation
A screenshot showing no visible consent banner may support the observation that no banner was visible within that captured frame at that time.
It does not independently prove that:
- No consent interface appeared earlier or later
- No prior preference was stored
- No geolocation or eligibility rule affected the interface
- No banner existed on another page or device
- Consent was legally required
- The visitor had not previously provided a preference
The screenshot becomes more useful when it is connected to a session record explaining browser preparation, stored state, region, page, actions, and timing.
Safer finding language: “No consent interface was visible in the captured viewport during the recorded initial-session observation.”
What Does “Log” Mean in a Website Review?
The word log is often used as though it describes one standard evidence format. It does not.
A log is generally a record generated by a tool or system. Its content depends on the layer being observed, the tool configuration, the available access, and the events that system was designed to record.
In a website tracking review, “logs” may refer to:
- Browser Network-panel entries
- Browser console output
- DNS resolver records
- Proxy traffic records
- Web-server access logs
- Application logs
- Content-delivery-network logs
- Consent-management-platform logs
- Tag-management debug output
- Scanner-generated event logs
A report should identify the exact source instead of referring broadly to “the logs.”
For example:
Artifact type: Browser Network log
Browser: Chrome
Session: Initial / no interaction
Page: Homepage
Capture window: 14:02:11–14:03:04 UTC
Export: Sanitized HAR
Limitations: Sensitive request fields excluded by browser export settings
This is more useful than:
Evidence: Logs
Browser-Network Logs
Modern browser developer tools include a Network panel that displays requests observed during the recording window. These entries may show information such as:
- Request URL
- Hostname
- HTTP method
- Status code
- Resource type
- Initiator information
- Timing details
- Request and response headers
- Query parameters
- Selected request or response data
- Cookie-related information
- Redirects
- Transfer size
The exact fields available depend on the browser, browser version, request type, capture settings, and whether sensitive information was omitted or preserved.
What browser-network entries may support
Within a defined session, browser-network entries may help support observations such as:
- A request to a particular hostname was visible
- The request occurred during a specified page journey
- The request appeared before or after a recorded reviewer action
- A redirect sequence was observed
- Selected request parameters or headers were visible
- A response attempted to set a cookie
- A particular script or request appeared to initiate another request
What they do not automatically establish
A browser-network entry does not automatically establish:
- Who legally controlled the destination domain
- What happened after the destination received the request
- Whether a parameter identified an individual
- Whether a transfer was legally permitted
- Whether a statutory definition applies
- Whether the observed behavior was caused by the website, browser, extension, campaign, user state, or another condition
- Whether the same request occurs for every visitor
Browser-network evidence should be described as an observation from the recorded environment, not as a complete representation of all network or server activity.
Chrome’s official documentation explains its Network-panel capture and HAR export functionality. Mozilla similarly documents that Firefox Network Monitor displays HTTP requests made by Firefox and can save the current Network log as HAR.
Browser Console Logs
The browser console may display messages produced by the browser, website scripts, frameworks, extensions, security controls, or developers.
Console output may include:
- JavaScript errors
- Failed-resource messages
- Content Security Policy warnings
- Cookie or storage warnings
- Deprecation notices
- Consent-platform debug messages
- Tag-management output
- Application-generated events
Console logs can help explain why a feature failed, whether a script encountered an error, or how a configured tool reported its state.
However, console output is not automatically an independent record of everything sent over the network. A script may write a message without sending a request, and a request may occur without producing a console message.
Console logs are therefore supporting artifacts rather than substitutes for browser-network evidence.
DNS, Proxy, and Server Logs
DNS records
A DNS record may help document that a domain name was resolved within the observed environment. Depending on the capture method, it may show:
- Queried hostname
- Resolution time
- Returned address
- Resolver response
DNS evidence generally does not show the complete HTTP request, request payload, response payload, or downstream use of information.
Proxy records
A configured proxy may observe traffic passing through that proxy layer. Depending on encryption, certificate setup, protocol, tool settings, and access, a proxy record may expose more or less detail than the browser’s Network panel.
A proxy capture should identify:
- The proxy tool and version
- The device or browser routed through it
- Certificate or interception configuration
- Capture filters
- Start and stop time
- Whether traffic could bypass the proxy
- Known protocol limitations
Server and application logs
Server-side logs may help document what a controlled system received or generated. They may include:
- Request time
- Requested path
- Response status
- Referrer
- User agent
- Session or request identifier
- Application event
- Error or processing result
Server logs require access to the relevant system and may not be available in an external website review.
They also represent the logging configuration of that system. A missing event may mean the event did not occur, but it may also mean it was not logged, was filtered, was rotated, or occurred in another service.
What Is a HAR File?
A HAR file is a structured HTTP Archive export commonly created from a browser’s Network tool.
It may contain entries representing requests visible in the recorded Network log, including selected information about URLs, methods, headers, timings, responses, cookies, and other fields supported by the browser’s export.
A HAR file should be described as an export of the recorded browser-network activity—not as a universal recording of the visitor, device, website, or internet session.
HAR is a format, not a conclusion
The file extension does not establish:
- Who created the file
- Whether the browser was correctly prepared
- Whether the capture began before the relevant event
- Whether the log was preserved across navigation
- Whether sensitive fields were included or removed
- Whether the file was edited after export
- Whether the recorded activity represents other users or sessions
- Whether an observed transmission was legally significant
Those questions require accompanying documentation and, where applicable, separate legal analysis.
What a HAR File Can Document
Within the scope of a properly recorded browser session, a HAR file may help document:
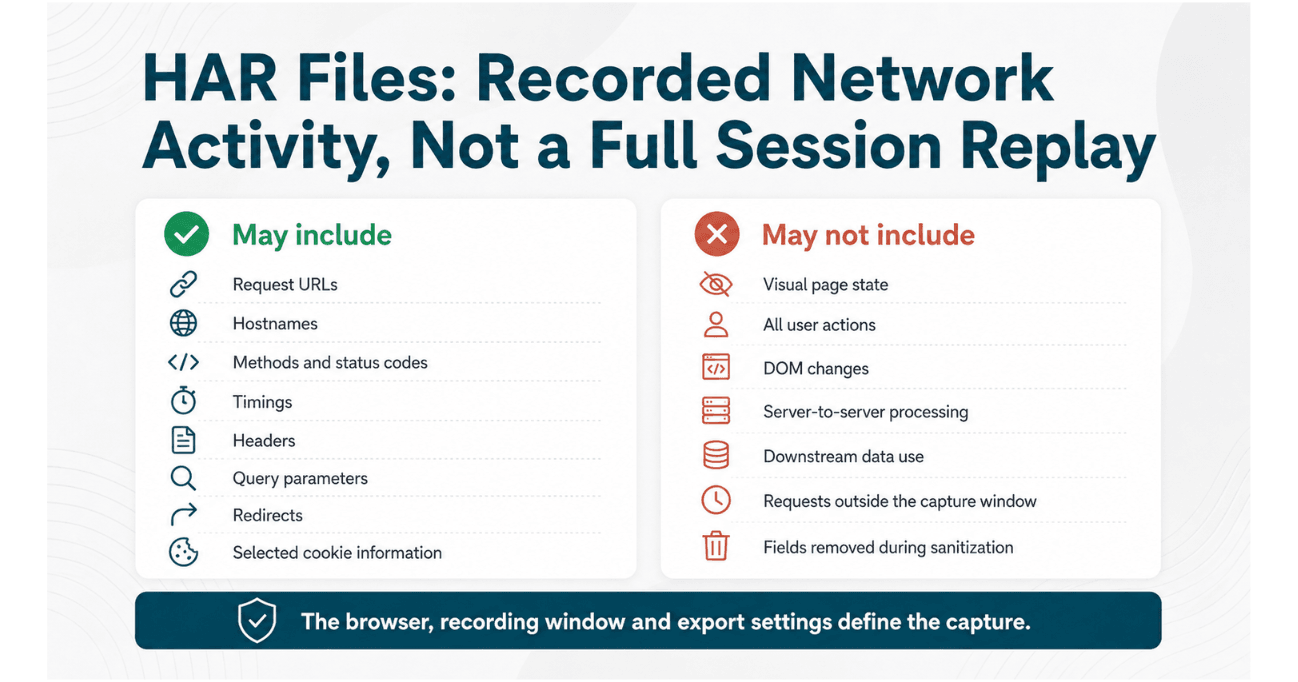
- Requests listed in the browser’s recorded Network log
- Request URLs and hostnames
- HTTP methods
- Status codes
- Request and response timing
- Redirect sequences
- Selected request and response headers
- Selected query-string parameters
- Selected cookie information
- Transferred resource types and sizes
- Initiator or connection information where exported
- Request ordering within the recorded log
Illustrative observation
A HAR entry might support a technical observation such as:
During the recorded initial homepage session, the browser Network log contained a request to the identified third-party hostname before the reviewer interacted with the visible consent interface. The exported entry included the page URL and a client-generated identifier. See HAR entry H-014 and screenshot S-006.
This language documents:
- The defined session
- The page
- The relative timing
- The observed hostname
- The visible fields
- The supporting artifacts
It does not declare that the request was unlawful, that consent was legally required, or that the identifier legally identified a person.
HAR files can support sequence review
HAR entries may help reviewers examine the apparent ordering of recorded browser requests. This can be useful when investigating:
- Initial page-load activity
- Requests occurring around a consent interaction
- Redirect chains
- Script and resource loading
- Requests following a form or button action
- Differences between separately prepared sessions
The phrase session replay should be avoided unless a separate replay technology was actually used. A HAR file is not a video and does not recreate the full visual, DOM, browser, or user-interaction state.
What a HAR File May Not Capture
A HAR export is limited by what the browser recorded and what the export preserved.
Depending on the browser, configuration, protocol, session, and export settings, limitations may include:
- Requests that occurred before recording began
- Entries cleared during navigation
- Activity outside the recorded tab or browser context
- Server-to-server communications
- Processing that occurred after a destination received information
- Activity hidden by encryption from an external tool
- Requests blocked before appearing in the log
- Browser-extension activity that altered the session
- Service-worker or caching behavior requiring separate interpretation
- WebSocket or other protocol details not fully represented by the export
- Response bodies or sensitive fields removed by sanitization
- Cookies or credentials excluded by browser defaults
- DOM changes and visual page state
- User actions not separately documented
- Browser storage that was not transmitted in a recorded request
Chrome sanitized and sensitive-data exports
Chrome DevTools excludes sensitive information from standard HAR exports by default. A separate preference can allow generation of a HAR containing sensitive data.
That creates an important review question:
Was the HAR exported in sanitized mode or with sensitive data, and is that distinction documented in the evidence index?
A sanitized export may be safer to share but may omit fields needed for a particular technical question. An export containing sensitive data may provide more detail but requires stricter handling, review, redaction, and access controls.
Neither option is universally “better.” The appropriate choice depends on scope, necessity, sensitivity, and the agreed evidence-handling process.
Why HAR Files Must Be Treated as Sensitive
A HAR file may contain sensitive values, depending on browser and export settings.
Potentially sensitive content can include:
- Session cookies
- Authentication tokens
- Authorization headers
- Request parameters
- Form-related information
- Account identifiers
- Email addresses
- URLs containing user or account context
- Response content
- Internal API endpoints
A reviewer should not assume a HAR is safe to email, upload, paste into a public tool, or attach to an unrestricted report.
Minimum handling precautions
- Review the file for sensitive values before sharing.
- Keep the original restricted.
- Create a separate redacted or sanitized working copy when necessary.
- Record which fields were removed or transformed.
- Limit access to people included in the agreed review process.
- Use secure transfer and storage appropriate to the material.
- Avoid publishing raw HAR files through public links.
- Do not overwrite the original with the redacted copy.
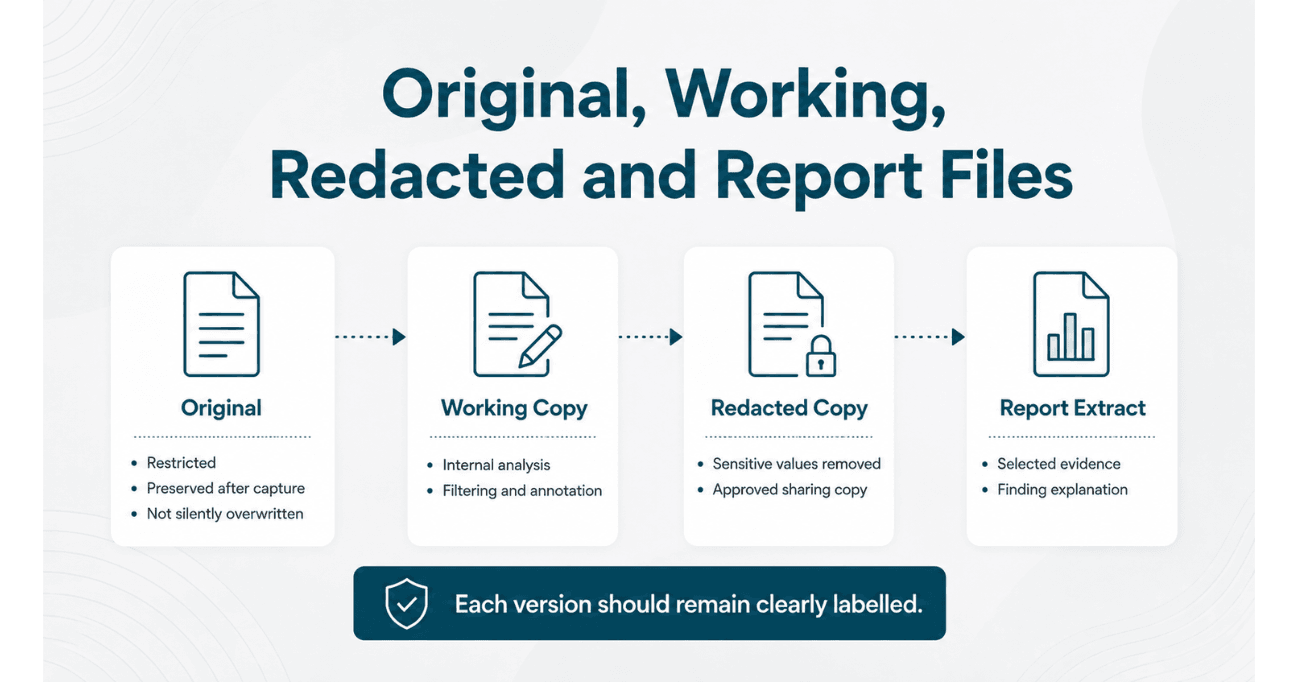
The evidence index should distinguish:
Original HAR: restricted, unchanged after intake
Working HAR: internal technical review
Redacted HAR: selected sensitive values removed
Report extract: limited entries reproduced for explanation
This distinction improves transparency without suggesting that redaction or hashing automatically establishes legal authenticity.
Cookies and Browser Storage as Supporting Records
Cookies, local storage, and session storage may contain values used for website functionality, preferences, analytics, authentication, advertising, security, or other purposes.
A browser-storage record may document:
- Cookie or storage-key name
- Associated domain or origin
- Observed value or redacted value pattern
- Expiration
- Path
- Secure, HttpOnly, or SameSite attributes
- Whether the item appeared before or after an action
- Whether the item differed between consent states
Storage presence does not explain purpose by itself
The presence of a cookie does not automatically establish:
- Who created it
- Why it was created
- Whether it was transmitted
- Whether it identifies a person
- Whether it is necessary or optional
- Whether consent was required
- Whether the website’s disclosure is accurate
- Whether a privacy violation occurred
Purpose classification may require reviewing:
- Request activity
- Script source
- Vendor documentation
- Website configuration
- Consent-platform categories
- Contractual or internal information
- Legal advice
Storage snapshots should be session-specific
A useful cookie or storage comparison identifies the session from which each record came:
Session A: Initial / no interaction
Session B: Reject non-essential
Session C: Accept selected categories
Session D: Returning visitor with stored preference
Combining values from multiple sessions into one undifferentiated list can hide when an item appeared and which action preceded it.
Evidence Format Comparison Matrix
| Artifact | May Help Document | Important Limitations | Useful Supporting Context |
|---|---|---|---|
| Page screenshot | Visible page, consent interface, form, widget, page state | Single visual moment; does not show complete network sequence | URL, timestamp, browser, session, consent state |
| Developer-tool screenshot | Selected request, header, cookie, storage key, console message | Only the visible selection; may omit surrounding entries and full fields | Underlying exported record and artifact reference |
| Browser Network log | Browser-observed requests, timings, status, selected fields | Limited to recording window and browser visibility | Session record, screenshot, export settings |
| HAR file | Structured export of recorded browser-network entries | Not a complete browser or server recording; fields may be sanitized | Capture protocol, original file, evidence index |
| Console log | Errors, warnings, debug output, policy messages | Not a substitute for network evidence | Page action, timestamp, script or request context |
| DNS record | Hostname-resolution activity | Does not normally show HTTP content or later processing | Network request and timing correlation |
| Proxy capture | Traffic visible through the configured proxy | Configuration, encryption, bypass, and protocol limitations | Tool configuration and browser route |
| Server log | Events recorded by the controlled server or application | Unavailable externally; limited by server logging configuration | Request IDs, retention policy, system context |
| Cookie or storage record | Values present in browser storage at a defined point | Presence alone does not establish purpose or transmission | Network entries and consent-state comparison |
The strongest artifact for a given finding depends on the question being investigated. There is no universal hierarchy in which HAR always outranks logs or screenshots.
Using Artifacts Together Without Overstating Them
Multiple artifacts may provide corroborating context for one technical observation.
For example:
- A page screenshot shows the visible consent interface.
- A browser-network entry shows a request during that session.
- A HAR entry preserves selected details about the request.
- A cookie comparison shows a related browser value after the request.
- An evidence index connects those artifacts to the finding.
This combination may make the technical sequence easier to understand and review.
However, corroboration should not be described as automatically making an observation:
- Legally admissible
- Authentic for every purpose
- Complete
- Representative of all visitors
- A statutory violation
- Proof of liability
- Immune from challenge
Prefer corroboration over “courtroom triangulation”
The phrase triangulation may be useful informally, but it is often overstated in marketing copy.
Safer wording is:
Multiple artifacts provide corroborating technical context for the recorded observation, subject to the documented scope and limitations of each artifact.
This preserves the practical value of combining evidence without predicting how a court, regulator, opposing expert, or other reviewer will treat it.
Finding-to-Artifact Traceability
A report becomes difficult to verify when it contains findings but does not explain where the supporting information can be found.
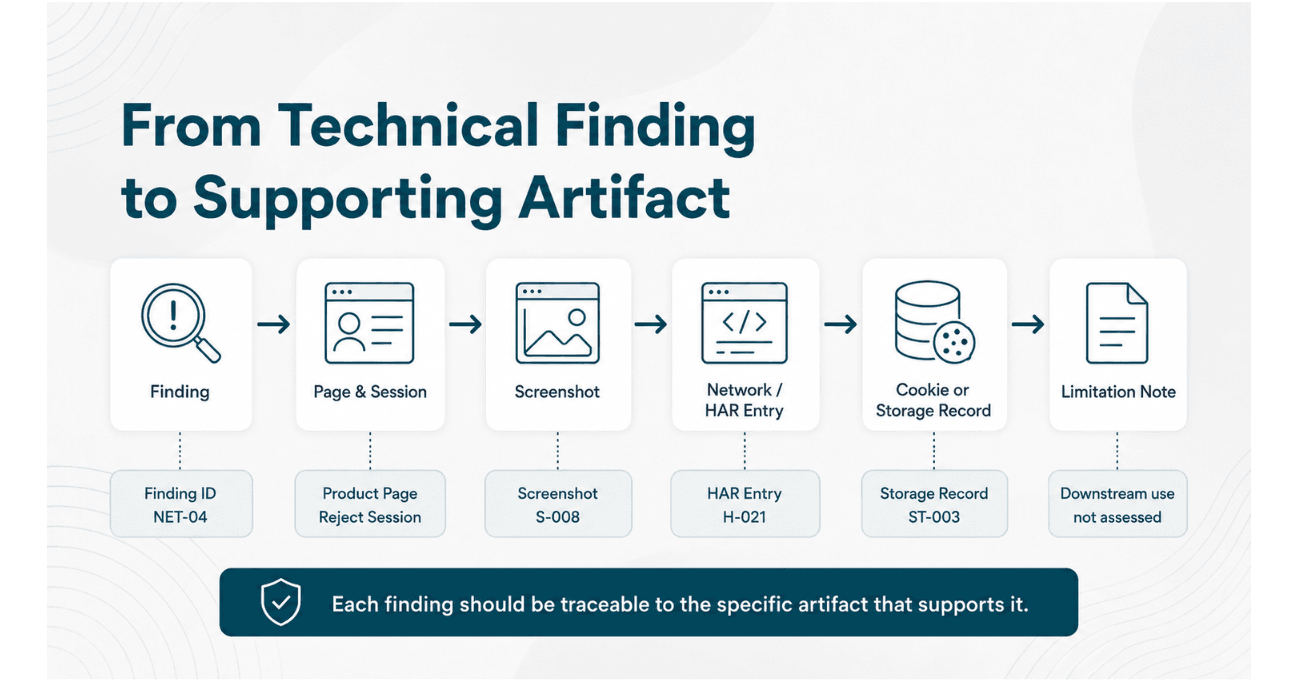
Each material finding should connect to:
- Reviewed domain
- Page URL
- Journey or reviewer action
- Session identifier
- Consent state
- Observation time
- Screenshot reference
- Network or HAR reference
- Cookie or storage reference
- Reviewer note
- Relevant limitation
Illustrative finding record
Finding ID: NET-04
Page: Product page
Session: B — Reject non-essential
Observation: Browser Network log contained a request to the listed third-party hostname after Reject.
HAR reference: B-HAR-021
Screenshot reference: B-SCR-008
Storage reference: B-STO-003
Limitation: Downstream processing and legal purpose were not assessed.
This structure allows another reviewer to follow the finding back to the relevant artifact without treating the finding summary as a substitute for the underlying record.
For more detail, read How to Preserve and Organize Website Tracking Evidence for Legal Review.
Original, Working, and Redacted Files
A technical evidence package may contain several versions of the same underlying artifact.
Original capture
The original capture is the file preserved after creation or intake. It should not be silently overwritten by later edits, annotations, formatting, or redaction.
Working copy
A working copy may be used for:
- Technical analysis
- Filtering
- Annotation
- Field extraction
- Vendor classification
- Request comparison
The working copy should remain distinguishable from the original.
Redacted copy
A redacted copy may remove or mask sensitive values before sharing. The record should explain that redaction occurred and, where appropriate, describe the categories of information removed.
Report extract
A report may reproduce selected rows, screenshots, request details, or storage values to explain a finding. That extract is a presentation layer, not the complete underlying file.
Recommended version labels
ORIGINAL — restricted capture
WORKING — internal review copy
REDACTED — approved sharing copy
EXTRACT — selected material included in report
Mixing these versions without labels can create confusion over which file was captured, reviewed, modified, or shared.
Hashes and Integrity References
A cryptographic hash can be used as an integrity reference for a specific file version.
If a file changes, its calculated hash will ordinarily change. This can help reviewers compare a later file against the version that was originally hashed.
What a hash may support
- Identification of a particular file version
- Detection of changes between hashed versions
- Verification that a transferred copy matches a recorded version
- Evidence-index references
What a hash does not prove by itself
A hash does not independently prove:
- Who created the file
- When the underlying event occurred
- Whether the capture process was correct
- Whether the file was already altered before hashing
- Whether the session conditions were accurately recorded
- Whether the file is complete
- Whether the file is legally authentic or admissible
- Whether the associated finding is correct
A hash becomes more useful when combined with:
- Capture documentation
- Timestamped intake records
- File-version labels
- Access history
- Transfer records
- Reviewer notes
- Preservation procedures
NIST’s digital-evidence preservation guidance emphasizes integrity and chain-of-custody considerations because digital files can be changed easily. A hash is one control within that broader process, not a replacement for it.
- NIST IR 8387: Digital Evidence Preservation
- NIST SP 800-86: Guide to Integrating Forensic Techniques into Incident Response
Why Session Preparation Matters
The same website may behave differently depending on the browser environment and visitor state.
Relevant conditions may include:
- Browser and version
- Operating system
- Device or viewport
- Visitor region
- Language
- Logged-in or logged-out state
- Existing cookies
- Stored consent preferences
- Browser cache
- Extensions
- Tracking-protection settings
- Global Privacy Control signal
- Campaign parameters
- A/B test assignment
- Previous page activity
A “fresh session” must be defined
Using an incognito or private window may reduce some stored state, but the report should not treat the phrase fresh session as self-explanatory.
The capture record should state what was done, such as:
New private browser window opened
Browser extensions disabled
Network log cleared
Preserve log enabled
Cache disabled during capture
No website interaction before recording
Homepage loaded directly
No consent selection made
If the review did not control or verify a condition, the report should say so rather than assume it.
Consent-State Testing and Evidence Separation
Website behavior may change after a visitor accepts, rejects, or customizes consent preferences.
A consent-state review may therefore use separately prepared sessions such as:
- Initial: No consent interaction
- Reject: Non-essential categories rejected
- Accept: Selected categories accepted
- Custom: Specific category combination selected
- Returning: Stored preference already present
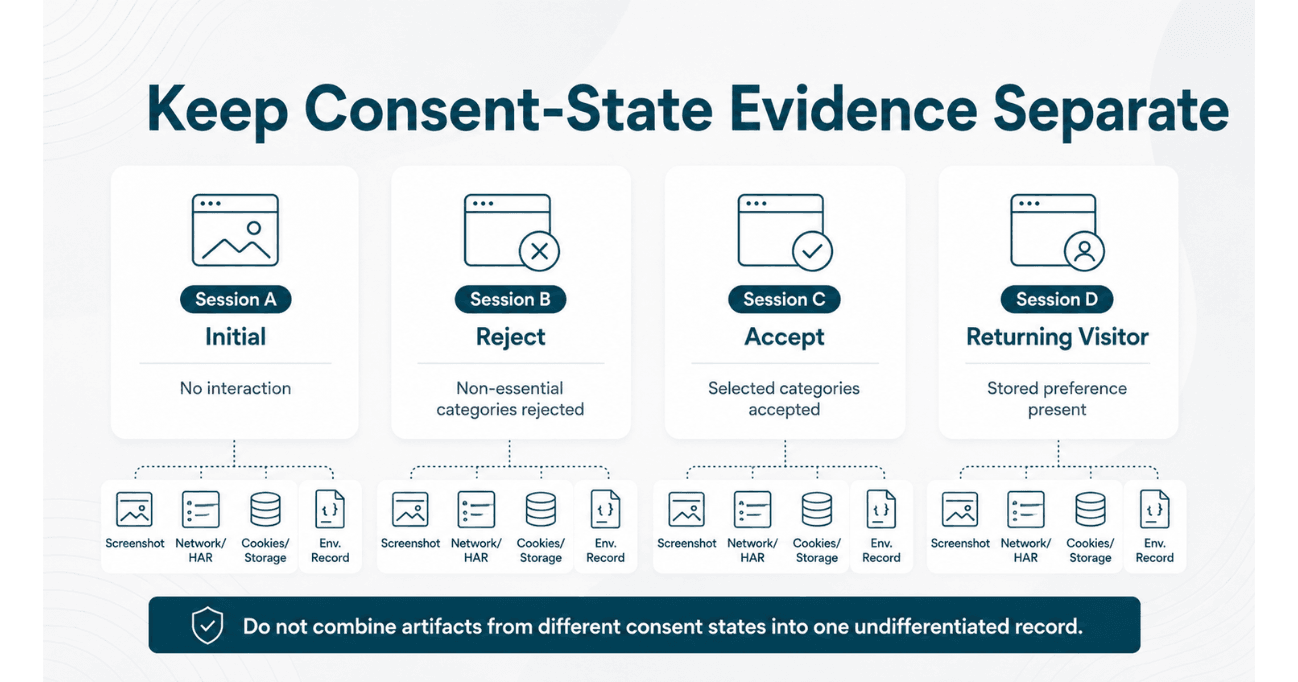
Each session should have its own:
- Screenshots
- Network capture
- HAR file where included
- Cookie and storage record
- Environment record
- Finding references
Artifacts should not be mixed between consent states without clear labeling.
Technical consent testing has legal limits
A technical review may document:
- Whether a consent interface appeared
- Which options were visible
- Which reviewer action was performed
- Which requests were observed in each session
- Which cookies or storage items differed
- Whether a preference appeared to persist
It does not independently determine:
- Whether consent was legally required
- Whether the interface language was legally sufficient
- Whether consent was informed or freely given
- Whether a particular technology required consent
- Whether another lawful basis or exception applies
- Whether a privacy violation occurred
For ecommerce-specific consent testing, review Cookie Consent Audits for Ecommerce Websites.
Automated Report vs Manual Evidence Audit
| Review Area | Automated Auditzo Report | Scoped Manual Evidence Audit |
|---|---|---|
| Primary purpose | Initial technical visibility and prioritization | Human-reviewed investigation of agreed technical questions |
| Initial page-load observations | Yes, within automated configuration | Yes, across agreed pages and journeys |
| Accept and Reject interaction | No | May be included where expressly scoped |
| Human verification | No | Yes |
| Screenshots | Report-level automated observations where generated | Agreed session and finding screenshots may be included |
| HAR or browser-network files | No downloadable raw-evidence package | May be included or reviewed where agreed |
| Cookie and storage comparisons | Initial automated observations | Human-reviewed comparisons across scoped states may be included |
| Finding-to-artifact review | Automated report structure | Human-reviewed traceability according to scope |
| Legal classification | Not provided | Not provided |
| Compliance certification | No | No |
An automated report is appropriate for initial visibility into website technologies and observed page-load behavior.
A Manual Evidence Audit is more appropriate when the review requires agreed visitor journeys, separate consent states, screenshots, browser-network analysis, HAR evidence, cookie or storage comparisons, and human-reviewed findings.
Review the website privacy audit plan comparison and Auditzo’s audit scope and limitations before selecting a review path.
What Technical Evidence Cannot Establish
Screenshots, logs, HAR files, cookies, and storage records may help document observable website behavior. They do not independently resolve legal questions.
Technical artifacts alone do not establish:
- That a privacy law applies to the organization or visitor
- That an observed value is legally personal information
- That a communication was legally intercepted
- That a script is legally a pen register or trap-and-trace device
- That consent was required
- That consent was legally valid or invalid
- That no lawful basis or statutory exception applies
- That a disclosure was legally adequate
- That a third party is legally a data broker
- That a cross-border transfer occurred
- That a user suffered legally cognizable harm
- That evidence is authentic or admissible
- That a violation or liability occurred
- That a claim or defense will succeed
These questions may require qualified legal advice, additional factual discovery, vendor records, contracts, configuration access, testimony, expert analysis, or other material outside the technical website capture.
Auditzo’s role: Auditzo documents technical observations and, where agreed, organizes supporting artifacts for legal, privacy, development, and remediation review. Auditzo does not provide legal advice, certify compliance, determine violations, guarantee admissibility, or predict legal outcomes.
Law firms and legal teams can review Auditzo’s website privacy evidence support for law firms.
Website Tracking Evidence Review Checklist
Scope
- Is the reviewed domain clearly identified?
- Are the reviewed pages and journeys listed?
- Is the capture date, time, and time zone recorded?
- Are excluded pages, systems, and questions disclosed?
Environment
- Is the browser and version recorded?
- Is the operating system identified?
- Is the visitor region documented?
- Are viewport, language, and login state recorded?
- Are cache, extensions, and stored-state conditions explained?
Screenshots
- Does each screenshot identify its page and session?
- Is the visible state explained without overstating it?
- Are developer-tool screenshots linked to underlying records?
- Are annotations distinguishable from the original capture?
Logs
- Does the report identify the exact type of log?
- Is the tool and version recorded?
- Is the capture window documented?
- Are filters, clearing, and preservation settings described?
- Are known blind spots disclosed?
HAR files
- Is the browser and export method recorded?
- Was the export sanitized or generated with sensitive data?
- Is the original preserved separately?
- Has the file been reviewed for credentials or personal information?
- Are selected HAR entries connected to report findings?
- Does the report avoid describing the HAR as a complete session replay?
Cookies and storage
- Are values tied to a specific session and consent state?
- Are domain, origin, and relevant attributes recorded?
- Are values redacted where necessary?
- Does the report avoid assuming purpose from the cookie name alone?
File handling
- Are original, working, redacted, and report copies distinguished?
- Are hash values tied to a specific file version?
- Are transfers, redactions, and transformations documented?
- Are sensitive files access-controlled?
Traceability
- Does each material finding reference supporting artifacts?
- Can the reviewer locate the relevant request, screenshot, or storage record?
- Are page, session, action, and timing clearly connected?
- Are contrary or inconclusive observations retained where relevant?
Limitations
- Does the report explain what was not captured?
- Are server-side and downstream activities excluded unless separately reviewed?
- Are one-session observations described as scoped rather than universal?
- Are technical observations separated from legal conclusions?
This checklist supports technical quality review. It is not a legal admissibility test, compliance certification, or substitute for matter-specific advice from qualified counsel.
Frequently Asked Questions
Is a screenshot enough to prove website tracking?
A screenshot may document visible page or developer-tool context at a particular moment. It generally does not preserve the complete request sequence, payload, browser-storage history, or server-side activity. The answer also depends on what the reviewer means by “prove.”
What is a HAR file?
A HAR file is a structured HTTP Archive export commonly created from the requests recorded in a browser’s Network tool. It may contain URLs, methods, timings, headers, cookies, response details, and other fields supported by the browser and export settings.
Does a HAR file record the entire browsing session?
No. A HAR file represents the browser-network entries recorded and exported within the capture window. It is not a complete video, DOM recording, device capture, server-side record, or universal history of everything that occurred.
Can HAR files contain sensitive information?
Yes. Depending on the browser and export settings, they may contain cookies, authorization values, request parameters, account details, form-related information, or response content. HAR files should be reviewed and handled as potentially sensitive.
Does Chrome remove sensitive data from HAR exports?
Chrome’s standard HAR export excludes sensitive data by default. Chrome also provides an option, when enabled in DevTools preferences, to export a HAR containing sensitive information. The selected export mode should be documented.
Are browser logs and HAR files the same thing?
Not exactly. The browser Network log is the recorded request list visible in developer tools. A HAR file is a structured export of information from that log. The export may not preserve every visible or sensitive field.
Do DNS logs show what information was transmitted?
DNS records generally help document hostname-resolution activity. They do not normally contain the complete HTTP request, request body, response body, or downstream use of information.
Can a screenshot prove that no cookie banner existed?
A screenshot can show that no banner was visible within the captured frame at that moment. Additional session records are needed to explain browser state, region, previous preferences, timing, and whether a banner appeared earlier or later.
Does hashing a HAR file make it authentic?
A hash can help identify a specific file version and detect later changes. It does not independently prove who created the file, whether the capture was correct, whether the file was altered before hashing, or whether it is legally authentic or admissible.
Should screenshots, logs, and HAR files be used together?
They can provide useful corroborating context because each documents a different layer of the session. The combination should still be described within its scope and should not be presented as automatically complete or legally conclusive.
Can an automated Auditzo report provide raw HAR files?
No. Auditzo’s automated reports do not include a downloadable raw-evidence package or human verification. A scoped Manual Evidence Audit may include agreed screenshots, HAR or browser-network evidence, cookie and storage comparisons, and other supporting files.
Can Auditzo determine whether evidence is admissible?
No. Auditzo provides technical observations and supporting records for review. Admissibility, authenticity, statutory application, consent, violations, liability, and legal strategy must be evaluated by qualified counsel.
Request a Scoped Technical Evidence Review
Auditzo supports law firms, privacy teams, website operators, agencies, and development teams that need clearer technical documentation of website tracking behavior.
A scoped Manual Evidence Audit may include:
- Defined pages and visitor journeys
- Browser, region, and environment records
- Initial, Reject, Accept, or custom preference sessions
- Page and developer-tool screenshots
- Browser-network review
- HAR files or selected HAR extracts where agreed
- Cookie and browser-storage comparisons
- Third-party hostname observations
- Finding-to-artifact traceability
- Original, redacted, and report-file distinctions
- Technical limitations
- Remediation-oriented observations
Discuss a scoped Manual Evidence Audit or review digital evidence for website compliance reviews.
For initial visibility into website technologies, cookies, browser storage, and third-party requests, teams can run an automated website audit.
Scope reminder: Auditzo provides technical evidence and observations for legal, privacy, development, and remediation review. It does not provide legal advice, certify compliance, guarantee completeness or admissibility, determine violations, or predict legal outcomes.
Official Technical References
- Chrome DevTools Network features reference
- Chrome DevTools Network and HAR preferences
- Mozilla Firefox Network Monitor documentation
- Mozilla Network Monitor HAR import and export controls
- NIST IR 8387: Digital Evidence Preservation
- NIST SP 800-86: Guide to Integrating Forensic Techniques into Incident Response
- Auditzo Audit Scope and Limitations
This article provides general technical information about website evidence formats. It does not provide legal advice, an evidentiary opinion, compliance certification, or a determination regarding any particular website, organization, claim, or legal framework.
Table of Contents
- Screenshots, Logs, and HAR Files Are Not Interchangeable
- What Screenshots Can Document
- What Screenshots Cannot Establish by Themselves
- What Does “Log” Mean in a Website Review?
- Browser-Network Logs
- Browser Console Logs
- DNS, Proxy, and Server Logs
- What Is a HAR File?
- What a HAR File Can Document
- What a HAR File May Not Capture
- Why HAR Files Must Be Treated as Sensitive
- Cookies and Browser Storage as Supporting Records
- Evidence Format Comparison Matrix
- Using Artifacts Together Without Overstating Them
- Finding-to-Artifact Traceability
- Original, Working, and Redacted Files
- Hashes and Integrity References
- Why Session Preparation Matters
- Consent-State Testing and Evidence Separation
- Automated Report vs Manual Evidence Audit
- What Technical Evidence Cannot Establish
- Website Tracking Evidence Review Checklist
- Frequently Asked Questions
- Request a Scoped Technical Evidence Review